“How do you meet reg. 28?”
// Compliance for regulated industries
Know every obligation is met.
Know every obligation is met.
Prove it in minutes.
Every obligation is linked to the policy, procedure and control that meet it, with the exact wording quoted, so you stop hoping and start knowing. Where there’s a gap you see it first, and AI drafts the fix for your team to approve.
// On the compliance team’s desk
Control_Register_v9.xlsx
Policies in Word, controls in a spreadsheet, links kept by hand
New rule · in force next quarter
A new rule nobody has traced to the controls it affects
Mapping project · statement of work
A costly one-off mapping exercise, dated by the next rule change
JMLSG Part I · ~800 obligations
Hundreds of obligations, and nobody can say which are met
The chain from obligation to control lives in people’s heads, and the auditors find the gaps first.
Your compliance team spends its time judging, not cross-referencing.
WhenTodayWith Whereas
Your framework needs mapping end to end
Today
A big outside project with consultants, and the result is a snapshot that soon dates.
With Whereas
Your team does it and keeps the mapping current as rules change.
A regulator asks how an obligation is met
Today
Weeks of manual cross-referencing, and the answer is often incomplete.
With Whereas
Answered in minutes, with the source wording behind every link.
A new regulation lands
Today
Someone reads it and works out from memory which policies it might touch.
With Whereas
Traced through to every policy, procedure and control it affects.
An auditor asks for evidence
Today
The auditor finds the gaps before the firm does.
With Whereas
You show the evidence, and you found the gaps first.
// Your name is on it
Know you’re covered before you sign.
Senior managers, MLROs and Qualified Persons answer to the regulator personally. Most sign off on a framework they can’t see end to end, and hope nothing is missing.
You see, obligation by obligation, what is covered, what is only partly covered and what isn’t covered at all. You know where you stand before anyone asks.
MLRO annual report · Sign-off · Example
I confirm that the firm’s systems and controls are adequate to meet its anti-money laundering obligations.
SignedMoney Laundering Reporting Officer
Trace every obligation to its control.
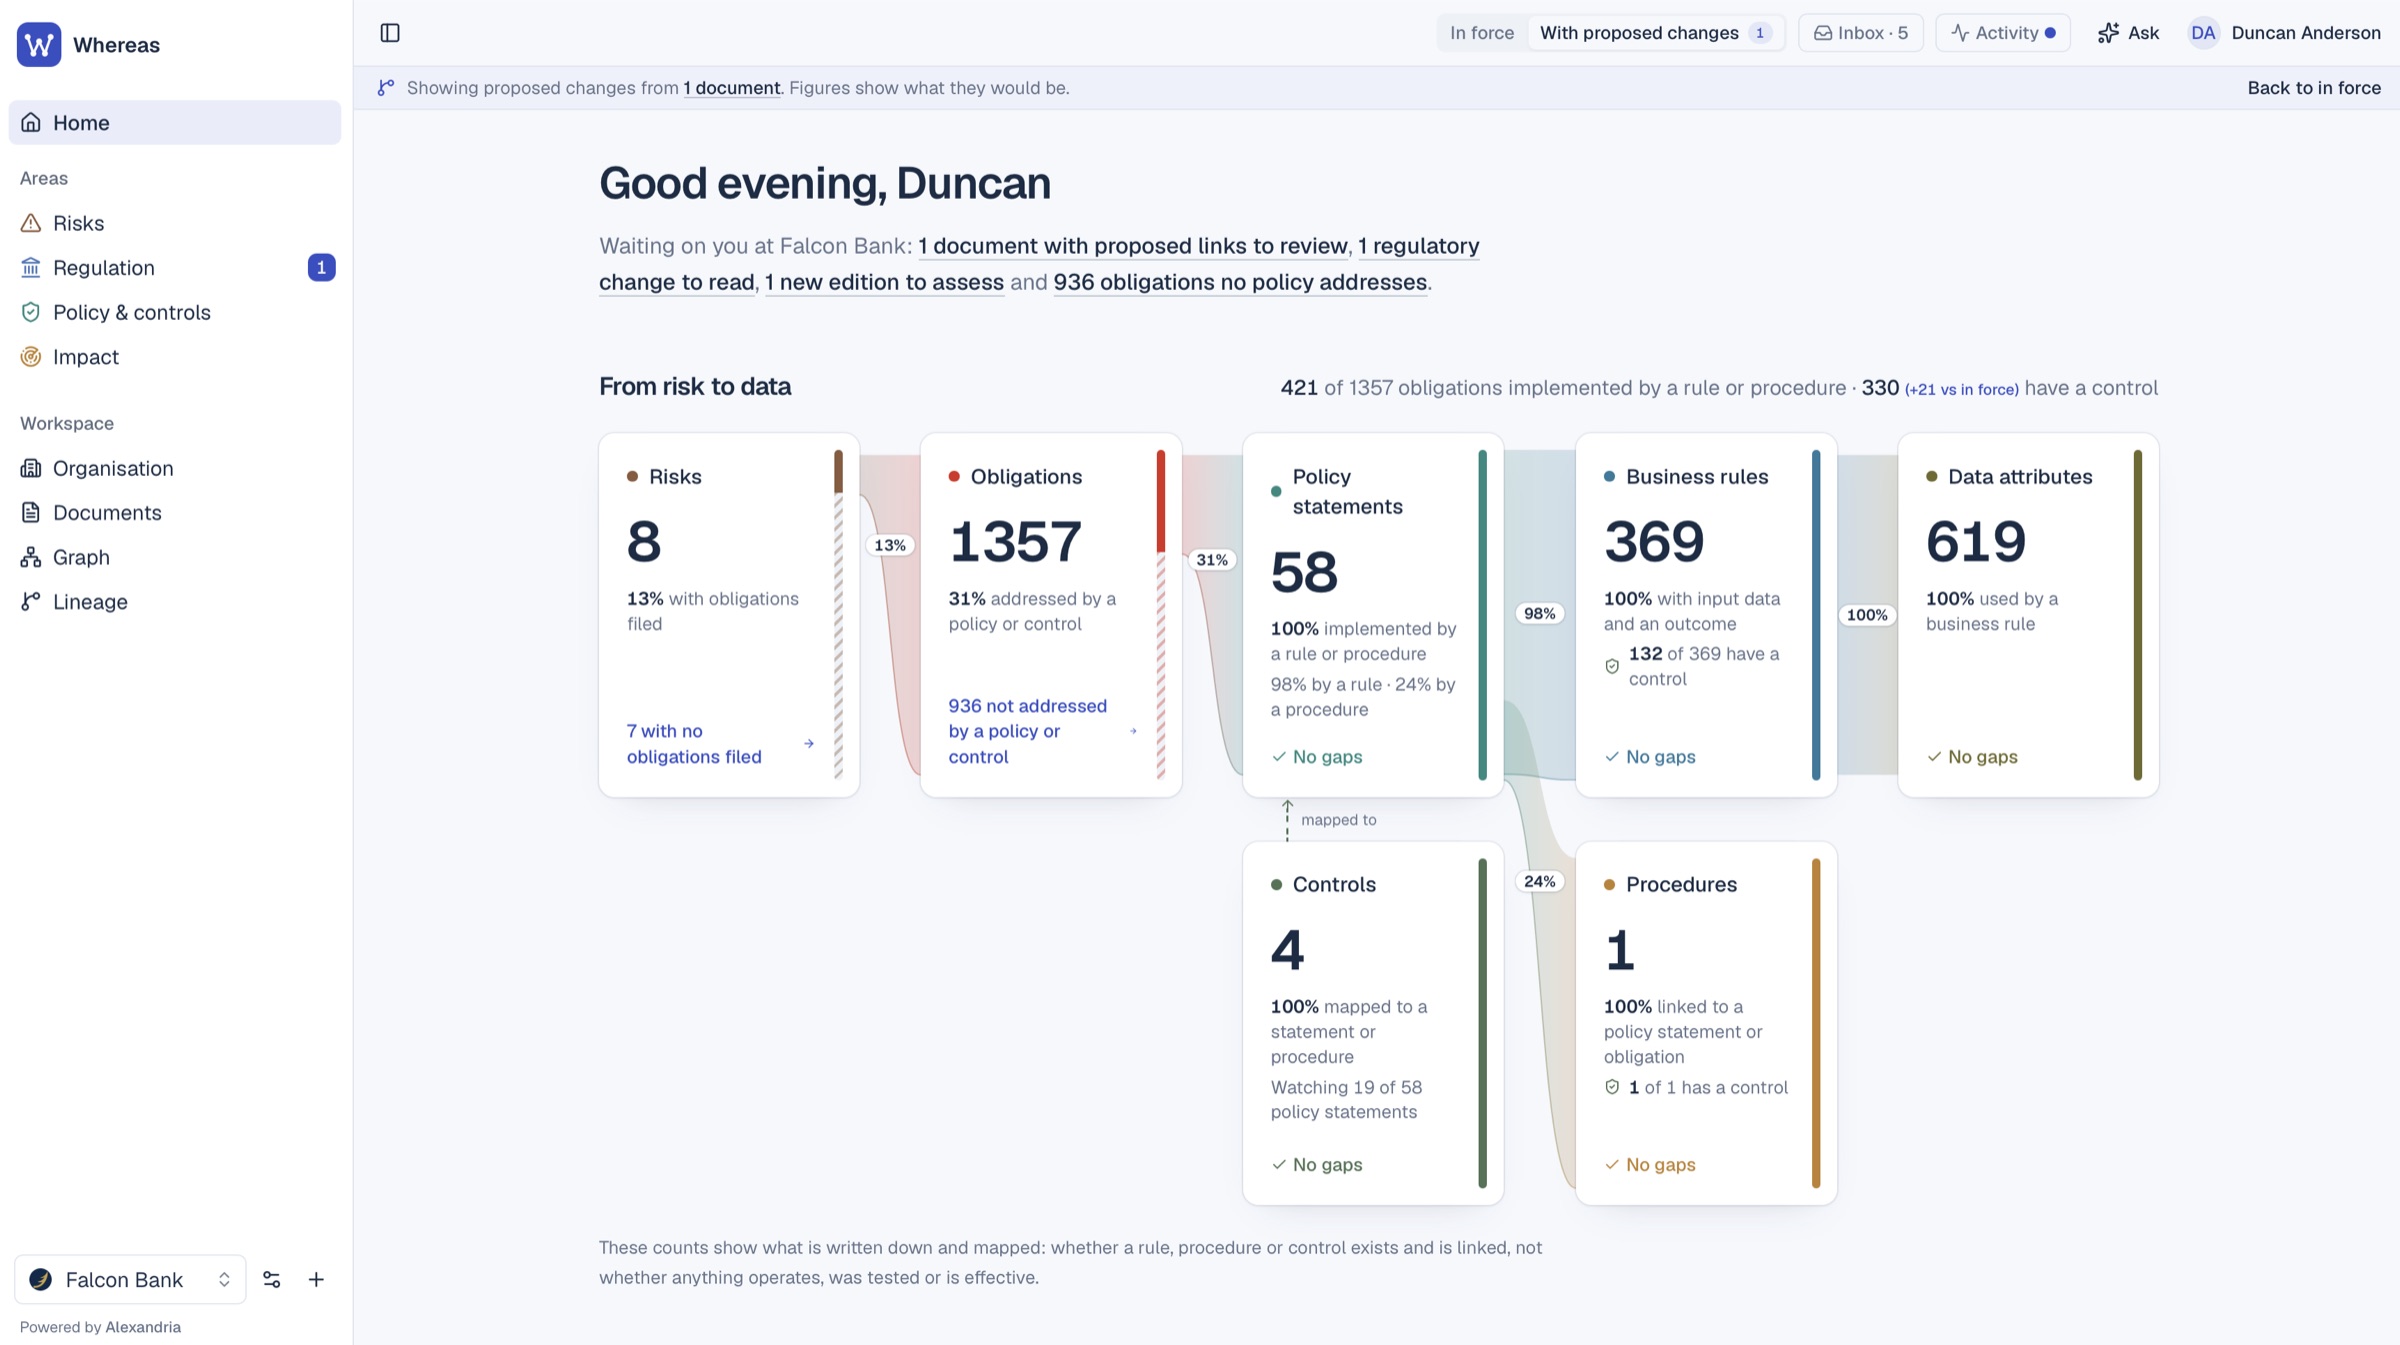
The chain from regulation to control becomes something you can see and query. Four steps take you from the regulations that apply to you to the controls that meet them, with people reviewing every link along the way.
Install the regulations that apply
AI extracts each regulation’s obligations clause by clause. An authorised person on your team reviews and approves the extraction, and from then on the rest of the team can build on it. Obligations that don’t fit your business, jurisdictions or products are set aside, with the reasoning recorded.
Read your own framework
The same AI reads your policies, procedures and controls, down to individual policy statements, procedure steps and control designs.
Review the proposed links
It then proposes which statements address which obligations, which procedures carry them out and which controls check them. Your people accept or reject each one. The lineage shows what is covered, partly covered and not covered at all.
Close the gaps
Draft a policy from the obligations it must address, or the set of controls a group of obligations needs. Control fact sheets cover owner, operator, steps, frequency, escalation and evidence, cite their obligations, and export ready for approval.
MLR 2017 · Reg. 28 · Customer due diligence · Paraphrased
The firm must identify the customer and verify their identity using documents or information from a reliable, independent source.
Partly covered
No control checks this. Policy statement CDD-03 reflects it and procedure KYC-2, step 4 carries it out. Nothing tests that verification happened. Draft a control fact sheet from this obligation.
Made by engineers who work in regulated environments.
Barnacle Labs builds AI systems for high-stakes, regulated organisations: in banking, insurance and biotech, and in a three-year partnership with the US federal government’s National Cancer Institute. Whereas is built with the same engineering discipline.
Grounded
Every link cites its source
Each obligation, link and draft points back to the exact wording it rests on, and nothing enters your framework until a person accepts it.
Approved
Your experts sign off every extraction
AI does the clause-by-clause extraction. An authorised person on your team checks and approves it before anyone else relies on it.
Your data
Your cloud, your AI providers
We set Whereas up with you, on the cloud you prefer and with the AI providers you’ve already approved. Your documents stay within arrangements your security team has signed off.
// Where it applies
Built for any rulebook.
The chain from obligation to policy, procedure and control is the same wherever there’s a regulator.
Anti-money laundering & financial crime
Dense obligations, frequent change, and a high cost when one is missed.
MLR 2017 · JMLSG guidance
Operational resilience
Important business services, impact tolerances and third-party risk, each needing evidence that controls work.
DORA · FCA SYSC 15A · PRA SS1/21
Insurance
Prudential and conduct obligations, from capital and governance to fair value and claims handling.
Solvency UK · Consumer Duty · ICOBS
Pharma GxP
Every requirement maps to an SOP and a control, and inspectors ask to see the evidence.
EU GMP Annex 11 · 21 CFR Part 11 · MHRA data integrity
Bring a regulation. We’ll show you the controls it needs, drafted and traced in front of you.
Book a demo